1. 4SO
  2. Products
  3. Workspace

Zero-trust workspace delivery

4SO Workspace

Work in the browser; execution and data stay off the user’s device.

Workspace separates the work environment and remote access from the user's endpoint; identity, policy, DLP, scheduling, session and execution sit in one manageable product model.

  • Linux Workspaces
  • RDP / VNC / SSH
  • DLP & Policy
  • Multi-zone
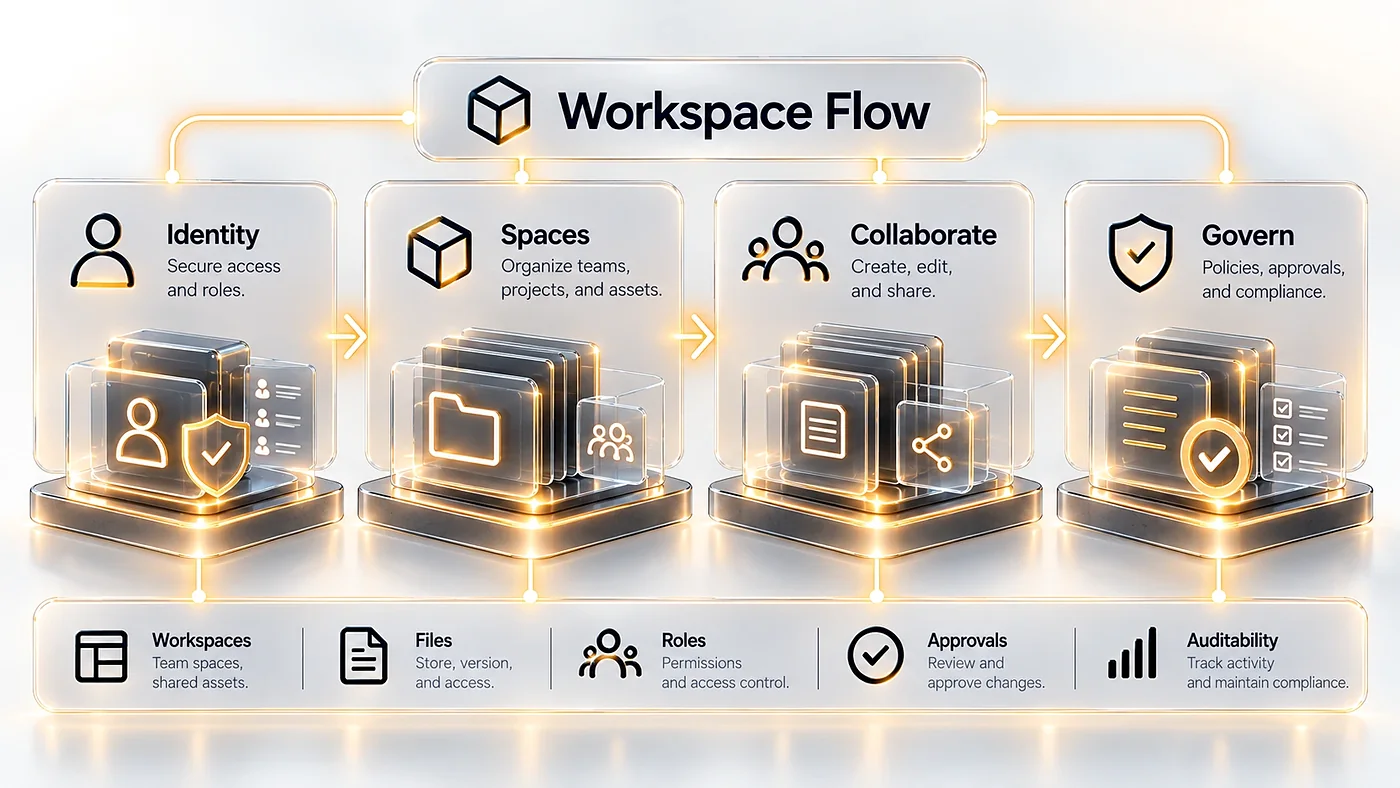
4SO Workspace flow: Identity, Spaces, Collaborate, Govern.
Who it is for
Organizations that must give staff, contractors or operations teams secure access without trusting their devices.
What it does
Delivers Linux browsers, desktops and applications plus RDP, VNC and SSH access in the browser, with enterprise identity, policy, data controls (DLP), session recording and audit.
Where it runs
Starts on a single server and grows with execution nodes across zones. Kubernetes is an option, not a prerequisite.
SCHEDULER · PLACEMENT · RECOVERYA secure workspace, only on an authorized and ready node
01

The user signs in with enterprise identity and access is checked against policy.

01Problem

Secure access gets hard when work runs on a trusted endpoint.

Teams usually run separate tools for Browser, Desktop, Remote Access, Policy and Session. Workspace brings them under one unified experience and separates protected execution from the user's device.

  1. 01

    The endpoint is not the place of trust

    The session and workload execution stay in a controlled environment; the endpoint is only the interaction layer.

  2. 02

    One entry point for several workspace types

    Browser, Linux Desktop/Application and RDP/VNC/SSH are all available from one web experience.

  3. 03

    Policy is part of the execution environment

    DLP, Identity, Network Path and Peripheral access are built into the product model.

  4. 04

    Session infrastructure is manageable

    Capacity, nodes, Scheduling, Audit and lifecycle are managed from the operator panel.

02Capabilities

A simple user experience, serious infrastructure behind it.

Workspace keeps User Experience and Infrastructure Operations capabilities side by side in one product.

  1. 01

    Browser, Desktop and App

    Disposable Linux environments for everyday work and controlled workloads.

  2. 02

    RDP / VNC / SSH

    Access to existing systems through the browser, without scattered clients.

  3. 03

    Enterprise identity and access

    Authentication, Authorization and scope for users and operators.

  4. 04

    Policy and data control

    File, Clipboard, Peripheral and Network Path can be controlled by Policy.

  5. 05

    Scheduling and Capacity

    Execution node selection, capacity and scale based on infrastructure state.

  6. 06

    Multi-zone Operation

    Extend the Execution Plane without turning the Control Plane into a workload runtime.

  7. 07

    Recording and Collaboration

    Session-level capabilities for observation, collaboration and Audit.

  8. 08

    Health, Capacity and Audit

    Operators follow infrastructure and session lifecycle from a single view.

4SO

Control Plane and Execution Plane are two independent roles. Workspace Intent is not locked to a specific execution environment; Single-node is a first-class deployment model.

03Deployment model

From a single server to a multi-zone Execution Plane.

The deployment model starts with one server and grows by adding execution nodes. Kubernetes is a deployment option, not a prerequisite for the user experience.

ProfileControl PlaneExecutionUse
Single nodeSame serverSame serverSimple start and small environments
Control + execution nodesDedicated Control PlaneMultiple execution nodesSeparate management from workspace execution
Multi-zoneCentral Control PlaneExecution in multiple zonesProximity to users and distributed capacity
HA Control PlaneMulti-nodeIndependent Execution PoolControl Plane redundancy and enterprise operations
04Lifecycle

A session is more than a launch.

From authentication to Scheduling, Policy enforcement, Resume, Recording and End, everything is part of the user and infrastructure lifecycle.

  1. 01Sign inAuthenticate
  2. 02ChooseSelect
  3. 03SchedulingSchedule
  4. 04StartLaunch
  5. 05Apply PolicyEnforce
  6. 06ContinueResume
  7. 07MonitorObserve
  8. 08FinishEnd
05Profiles

The access type changes; the product experience stays the same.

Users enter from a single Catalog, and differences in the execution environment are managed behind the same process.

  • Browser Workspace

    A controlled Linux browser for accessing web applications.

    • Session separated from the endpoint
    • Policy on File/Clipboard/Network
    • Ephemeral lifecycle
  • Linux Desktop / App

    A Linux desktop or application delivered through streaming.

    • Containerized execution
    • Catalog-based launch
    • Capacity-aware scheduling
  • Remote Systems

    Secure connection to existing systems from the browser.

    • No local client dependency
    • Central access policy
    • Unified session audit
  • Single-node

    Control and Execution on one host.

    • Simplest installation
    • The same full UX
    • A growth path without changing the user model
  • Distributed

    Independent execution nodes under one Control Plane.

    • Capacity pool
    • Node health
    • Workload placement
  • Multi-zone

    Execution closer to the user or resource.

    • Location-aware scheduling
    • Failure-domain separation
    • Central policy
Technical reference

Architecture, workflows and operations in detail

For engineers who want to know how the product works underneath: components, boundaries, failure behavior and the operations it runs.

06Architecture

Control Plane and Execution Plane are deliberately not the same.

Intent and Policy stay in the Control Plane; agents carry out management, and the real session runs in the Execution Plane.

  1. USER
    Browser ExperienceAuthentication, Catalog, Launch/Resume and session end.
  2. CONTROL
    Workspace Control PlanePostgreSQL, Identity, Policy, Scheduling and durable operations.
  3. AGENT
    Authenticated Agent PlaneOutbound-first management with defined trust and state.
  4. EXECUTION
    Workspace execution environmentBrowser/Desktop/Application runtime and Remote Session.
LayerComponent / ProtocolRoleContract
State AuthorityPostgreSQLWorkspace intent, Session lifecycle, Policy, Node/Capacity and durable operationsUI and Agent do not create independent sources of state
Control PlaneGo services + Product APIIdentity, Authorization, Scheduling, lifecycle and auditControl Plane ≠ Execution Plane
Agent PlaneOutbound-first mTLS agentsNode management, observed state and bounded action executionAgent authority passes through the Product API/RBAC
Linux StreamingKasmVNCBrowser/Desktop/Application workspace streamingProtected execution stays on the Execution Plane
Remote AccessApache Guacamole ecosystemRDP / VNC / SSH from the browserRemote protocols sit behind the same Identity/Policy surface
TECH

Install & Runtime Contract. Workspace is not installed from a source checkout; the release artifact, preflight and resume boundary are part of the Product Contract itself.

BoundaryMechanismTechnical contract
Release artifactMANIFEST.json + SHA256SUMSAPI, Controller, Edge, CLI, migration and runtime inputs are delivered as a deterministic bundle.
Preflight 1Read-only boundary preflightThe release cache, host and installation boundaries are checked before any mutation.
Release authorityExact cached artifactThe verified artifact, with an identity bound to the commit/manifest, is published into the installer-owned cache; unsafe hard links and permissions are rejected.
Preflight 2Cached-artifact preflightThe same exact artifact is checked again before convergence so source and runtime paths do not diverge.
Host exposureLoopback TLS edgePostgreSQL and the Control API are not host-published; the canonical product endpoint stays on the bounded TLS edge.
Diagnosis / resumeDoctor + status-jsonresume_required and last_safe_resume_point are reported from the durable owner boundary, not from browser guesswork.
ExecutionDocker Engine first · Kubernetes optionalKasmVNC and Guacamole run in the Execution Plane.
07Workflows and failure

A session is not a momentary request; both the operation and the observed runtime are tracked.

Launch, Stop, Restart and Recovery go from the Product API to Operation/Outbox, and session state is observed separately from request state.

  1. 01RequestREQUESTED
  2. 02AdmissionADMITTED
  3. 03RuntimeRUNNING
  4. 04SuccessSUCCEEDED
SCHEDULER BRANCH

Placement based on Policy and Capacity

A session is created only on an authorized, ready node.

SESSION REQUEST
↓
POLICY +
CAPACITY
↓
NODE A
NODE B
NODE C
Scheduler → agent admit → runtime launch → observed ready
No capacity → admission blocked, not random placement.
ACCESS SPLIT

Linux Workspace or Remote Protocol

Identity/Policy is shared; the Execution Path differs.

AUTHENTICATED USER
↓
RESOURCE
POLICY
↓
KasmVNC
LINUX
↙ ↘
GUACAMOLE
RDP/VNC/SSH
One Identity/Policy surface · two protocol runtimes
KasmVNC and Guacamole are two runtime paths under one Control Plane.
RECOVERY FORK

Recover Runtime or Cleanup

The failure class determines whether repair or cleanup is performed.

FAILED / STALE SESSION
↓
CLASSIFY
↓
RECOVER
RUNTIME
↙ ↘
RECOVER
CLEANUP
↓
OBSERVE + CONVERGE
Unknown runtime state is resolved through Agent read-back before any retry.
  1. Flow 01

    Launch Workspace

    The session is actually created only after admission and scheduling.

    1. Identity
    2. Policy
    3. Catalog
    4. Capacity
    5. Scheduler
    6. Session Ready

    Failure and recoveryThe UI does not guess the session outcome from an accepted operation.

  2. Flow 02

    Remote Access

    The browser connects to the protocol runtime without the endpoint becoming the place of trust.

    1. User Login
    2. Resource Scope
    3. Policy
    4. Guacamole Route
    5. RDP/VNC/SSH
    6. Session Observe

    Failure and recoveryA policy failure or target failure stops the access path before session attach.

  3. Flow 03

    Session Restart

    A restart is linked to a traceable successor session.

    1. Source Session
    2. Restart Admit
    3. Stop Boundary
    4. Successor Create
    5. Health
    6. Attach

    Failure and recoverySource and successor correlation is preserved; an incomplete restart is not reported as success.

  4. Flow 04

    Runtime Recovery

    Recovery is not the same as an ordinary restart.

    1. Failure Detect
    2. Classify
    3. Recover Runtime
    4. Agent Action
    5. Observe
    6. Converge

    Failure and recoveryThe recovery attempt and retry count remain in history.

  5. Flow 05

    Node Drain / Remove

    Session infrastructure changes without orphaning workloads.

    1. Node Health
    2. Capacity Gate
    3. Stop Placement
    4. Drain Sessions
    5. Remove
    6. Reschedule Verify

    Failure and recoveryA node with active sessions is never silently removed.

Additional operational flows

Policy and Capacity are also part of the session runtime, not peripheral settings.

  1. Flow 06

    Policy / DLP Change

    A policy change remains traceable from the authority to its enforcement on the session.

    1. Policy Intent
    2. Scope / RBAC
    3. Conflict Check
    4. Persist Policy
    5. Agent Propagate
    6. Session Apply
    7. Observe

    Failure and recoveryPartial policy application goes to Reconcile; the session must not continue with a silent bypass and no evidence.

  2. Flow 07

    Add Execution Node

    New capacity enters the pool only after Trust, Health and Scheduling eligibility.

    1. Node Identity
    2. Preflight
    3. Agent mTLS
    4. Register
    5. Capacity Observe
    6. Scheduling Eligible
    7. Placement Verify

    Failure and recoveryAn unhealthy node, or one without a valid Agent identity, does not become eligible for placement.

Action / FlowAdmission / PreconditionsExecution / LockSuccess CriterionFailure / Recovery
Launch WorkspaceActor/Project permission, Catalog entry, Policy and Capacity must all allow itIdempotency-Key → durable Operation/Outbox → scheduler/AgentA Session ID and observed session/runtime state are returned for the same WorkspaceA failure can create a retry/recovery event; the UI does not guess session state from the Operation
Stop SessionExisting session and valid permissionA separate stop Operation goes to the Agent/runtimeThe session is no longer serving/running and the Operation becomes terminalCancellable before lease; after a side effect the outcome must be reconciled from the runtime
Restart SessionValid source session and restart allowedThe Operation is linked to the restart attempt and the successor sessionThe successor session is observed and usableSource/successor correlation is preserved; a failure does not report the previous session as a new success
Recover RuntimeSession has a failure/recovery conditionExplicit RECOVER_RUNTIME action; a generic restart does not replace recovery semanticsThe runtime is observed-ready again and the session leaves the recovery stateThe recovery attempt and the time of the last retry remain in history
Recover CleanupProvable stale/partial runtime cleanupExplicit RECOVER_CLEANUP action on the same sessionHalf-finished resources are cleaned up and the authority converges with the runtimeCleanup without evidence is not turned into a new session or a success
Node Capacity LifecycleNode/Execution Plane health and capacity are checked before Add/Drain/RemoveScheduling is separate from, but coordinated with, the node lifecycleRetained sessions are healthy and placement/capacity is read from observed stateDrain/Remove must not silently orphan an active session; reconciliation is the return path
FLOW

Cancellation is possible only at the early safe boundary: the Operation is in REQUESTED/ADMITTED, has no lease owner and has not crossed the side-effect boundary. History keeps Launch/Stop/Restart/Recover, the retry count and the latest recovery.

08Operations catalog

Operations follow two journeys: the user’s and the infrastructure’s.

The user sees the session; at the same time the operator manages capacity, nodes, Policy and Audit.

  • Publish WorkspaceDefine a workspace and publish it to the permitted scopes.
  • Launch / ResumeStart or resume a session with Identity and Policy.
  • Assign AccessBind users/groups to a workspace and Policy.
  • Observe CapacityView Health, Load and Execution Plane capacity.
  • Add execution nodeExpand capacity without changing the user experience.
  • Drain / Remove execution nodeControlled removal of a node from Scheduling and the lifecycle.
  • Record / AuditTrace sessions and operational events.
  • Scale InfrastructureGrow from Single-node to a distributed architecture.

Separate the workspace from the endpoint; keep the user experience simple.

4SO Workspace turns secure access from scattered connections into one manageable product.